What we do with your technology stack
Our goal is simple: be the fastest, best-informed attacker on your attack surface. For every asset you expose, we:
- Identify the technologies in use — server operating systems, web frameworks, appliances, libraries and more.
- Classify them so we can reason about your stack at scale.
- Assess the one question that matters: can we exploit this right now?
- Re-check continuously as your technology changes, because tomorrow’s exploit may land on today’s safe version.
See every technology, in one place
Active Focus gives you a live overview of every technology identified across your attack surface — web frameworks, servers, CDNs, security headers, third-party services and more, each with the assets it appears on. It is an ever-expanding picture: as your estate changes and as we classify more, the overview grows with it.
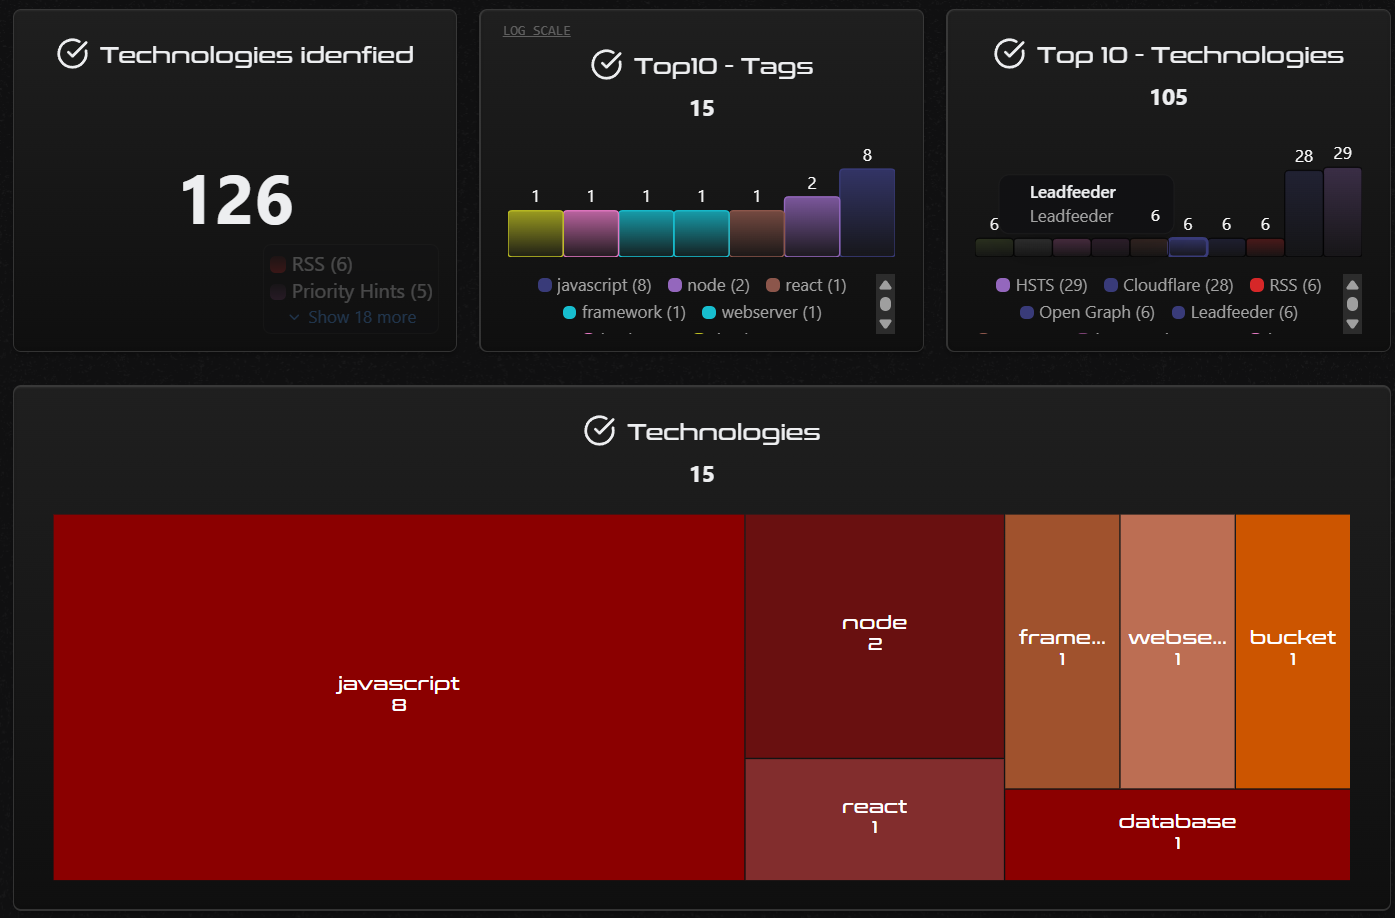
That inventory is not just for visibility — it is how we move fast on new threats. River Security correlates vulnerabilities to technology in several ways, and the overview is one of the most powerful: when a serious CVE or emerging threat breaks, we pivot straight to the technology view and answer, in seconds, which customers and which assets run the affected technology? That turns a headline vulnerability into a targeted, prioritised action instead of a scramble.
We also subscribe to vendor and community security bulletins for the technologies that represent our customers. When a vendor announces something you need to act on, you don’t get a raw feed to triage yourself — you get an immediate notification with a suggested plan of action, and a two-way dialogue with our team on how to handle it.
The overview also makes the case for restraint: the smaller and more consistent your technology footprint, the fewer future vulnerabilities can ever apply to you — keeping your technology mix lean is one of the most durable ways to defend yourself against tomorrow’s unknown CVEs.
We alert on risk, not noise
We pull technology data from scanners, OSINT sources and commercial vulnerability tooling, then normalise it and put it in front of penetration testers. That human step is the difference between a scanner and Active Focus: if a weakness cannot actually be abused, we will show you the information, but we will not page you about it. Alerting on unexploitable findings is crying wolf, and it buries the signals that matter.
Winning the OODA loop
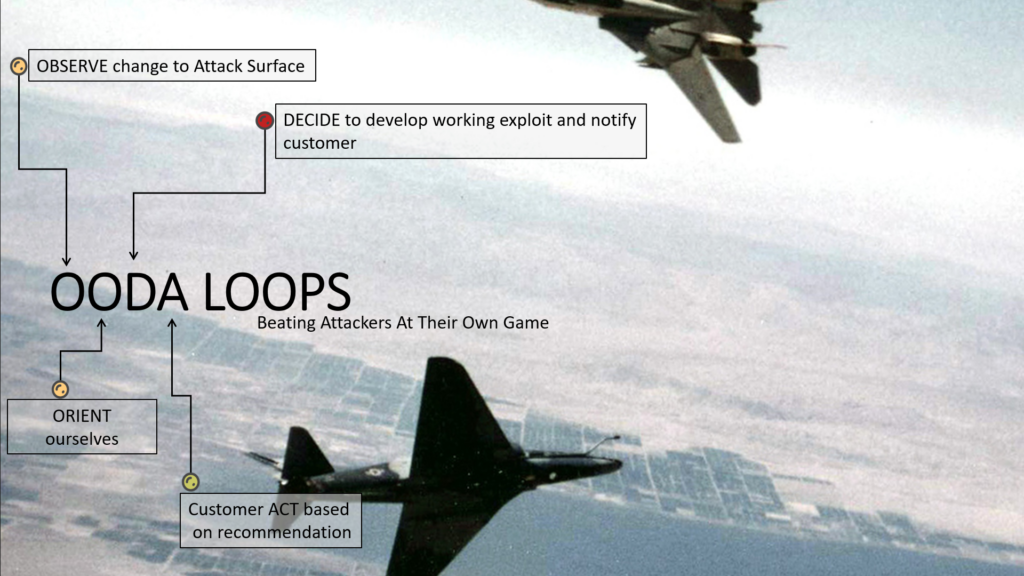
The dog-fight above is how we think about it. Whoever observes, orients, decides and acts fastest wins — the OODA loop. By continuously assessing risk, constantly testing for ways in, and operating as close to real threat actors as possible, our Offensive Security Operations Center keeps you ahead of the attackers watching the same ageing technology. Always-on, always looking, from the attacker’s side of the wall.