The path least travelled
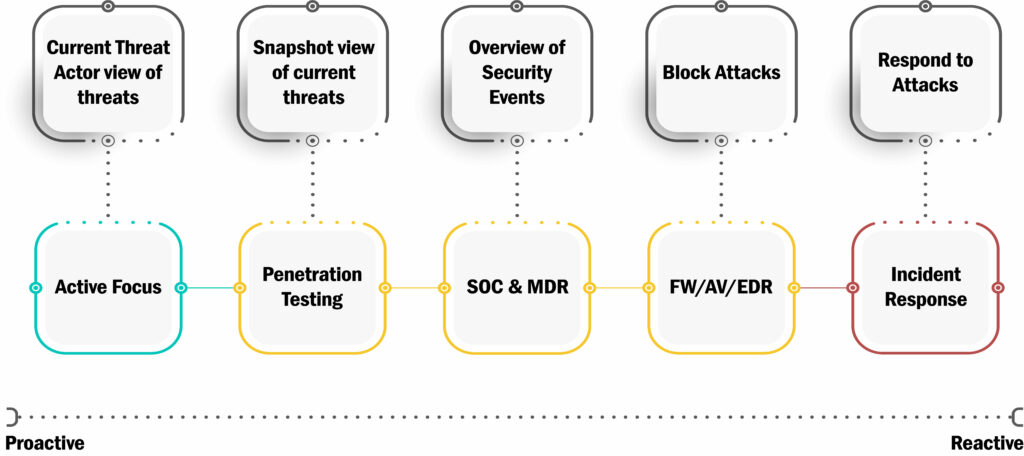
Attackers look for what we call the path least travelled: the systems nobody remembers, the ones without governance, patch management or monitoring. A forgotten subdomain pointing at an unpatched box is worth more to them than your well-defended front door. Active Focus continuously tracks what your DNS reveals — new systems as you provision them, old systems still lingering — so those forgotten assets surface to us before they do to a threat actor.
The DNS value chain for attackers
Attackers work down a predictable chain, and each link is attack surface:
- DNS names are discovered.
- Names resolve to IP addresses (IPv4 or IPv6).
- IP addresses may have firewall openings, exposing network services over TCP and UDP.
- Those services run applications, which may carry exploitable vulnerabilities.
Our job is to walk that chain from an offensive point of view — quickly, continuously, and across both your new and existing attack surface — so risk is uncovered and addressed before anyone else gets there.
How we discover domains
The most common technique is brute-forcing DNS with wordlists of interesting names — asking a server whether each one exists:
customer1.riversecurity.eu?admin.riversecurity.eu?ftporsftp.riversecurity.eu?
These queries are automated and can run into the millions, hunting for anything that resolves to an IP an attacker can then scan and attack. We run the same playbook, first.
Certificate Transparency logs
Certificate Transparency (CT) logs are one of the richest real-time sources of domain data. Certificate Authorities publish every certificate they issue, and Active Focus monitors these logs live. The scale is staggering — roughly 35 million new domains with an SSL/TLS certificate are created every week — which is exactly why watching them continuously, rather than checking now and then, is what makes the difference. Crucially, we don’t just watch your domains — we watch your brand. Instead of tracking only riversecurity.eu, we track riversecurity, which surfaces far more than you formally manage: shadow IT and, often, phishing domains.
Catching a phishing domain this early in the attacker’s kill chain is a gift. It lets us proactively block it in the firewall and pull the legs out from under the campaign before it ever launches. Proactivity for the win.
Integrations: domains straight from the source
Outside-in discovery finds what attackers can find. Integrations close the gap on everything else. Active Focus lets you connect your cloud environments and domain registrars directly, so authoritative domain and DNS data flows in continuously — no brute-forcing required, and nothing missed because it never showed up in a public source.
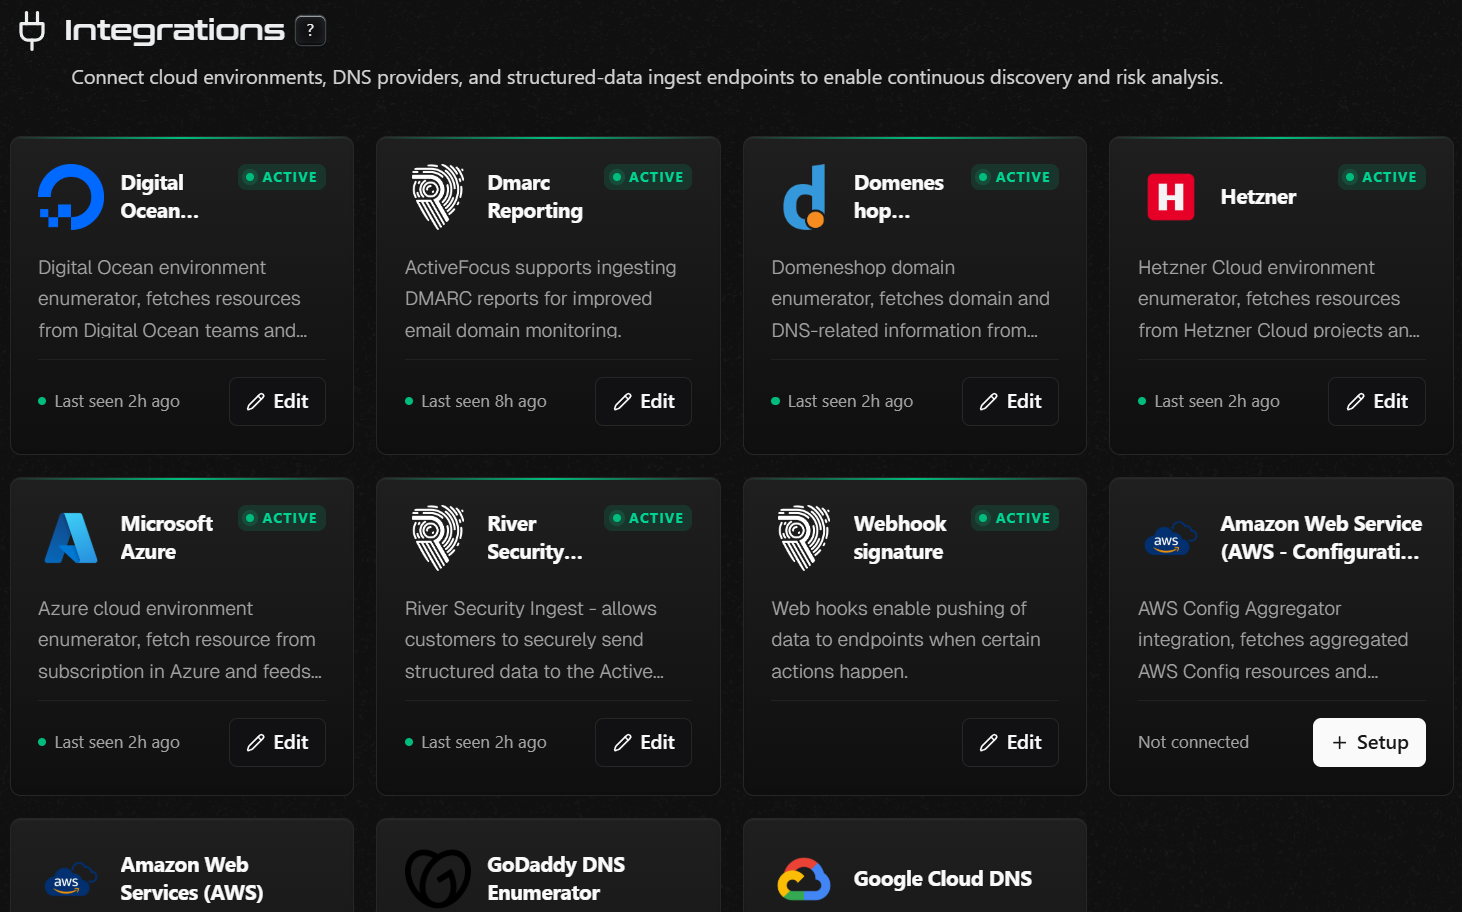
Customers share domains with us the way that suits their environment:
- Cloud environments — AWS, Microsoft Azure, Google Cloud, Digital Ocean and Hetzner enumerators pull resources and their domains straight from your accounts.
- DNS providers and registrars — integrations for providers such as Domeneshop, GoDaddy and Google Cloud DNS bring your registered domains and DNS records in directly.
- Direct and structured ingest — River Security Ingest, webhooks and DMARC report ingestion let you securely push domain and email-domain data to Active Focus as it changes.
Combining continuous outside-in discovery with authoritative inside-out data from your own environments gives Active Focus the most complete, always-current view of your domain attack surface — so nothing you own becomes the path least travelled.